Build Security Into the Software Delivery Lifecycle
Integrate security checks, identity, secrets, policy and supply-chain controls into CI/CD and cloud-native delivery workflows so teams can identify risk earlier without turning every release into a manual security gate.
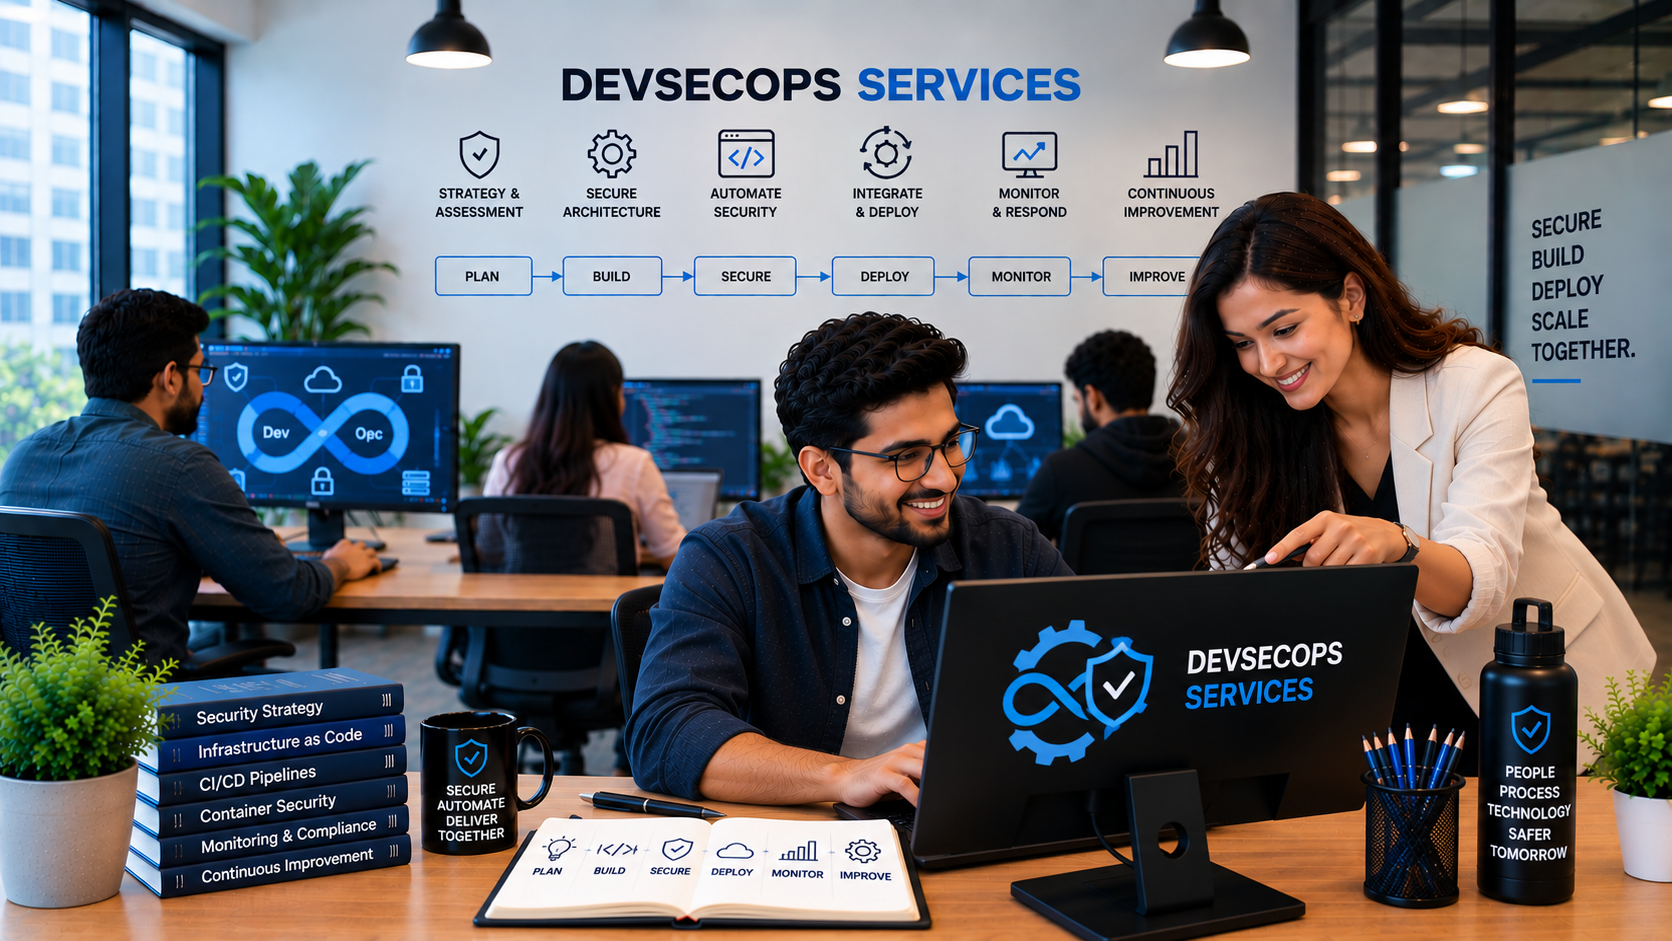
Shift Security Into the Engineering Workflow
Make secure delivery part of the path developers already use.
DevSecOps works best when security requirements become repeatable engineering controls instead of late-stage checklists. We integrate suitable code, dependency, secret, container, infrastructure and deployment checks into the software lifecycle, with risk-based escalation for findings that need human review.
Three benefits.
Earlier Feedback
Automated Guardrails
Risk-Based Delivery
What We Build
Secure CI/CD Pipelines
Build and deployment workflows with integrated security checks.
Application Security Automation
Automated code, dependency and secret scanning integrated into engineering workflows.
Cloud Security Engineering
Identity, secrets, configuration and policy controls for cloud workloads.
Container Security
Image, dependency and Kubernetes delivery controls.
Infrastructure Security
IaC validation and policy checks for cloud resources.
Secure SDLC Programs
Practical security activities mapped across design, development, testing and release.
Secure CI/CD Pipelines
Put the right security check at the right point in delivery.
Not every finding should block every build. We design pipeline controls around risk, environment and signal quality, using fast checks early, deeper analysis where appropriate, and explicit exception or review paths so teams can fix meaningful issues without drowning in noisy gates.
Code
Dependencies
Secrets
Containers
Infrastructure
Release
Core DevSecOps Capabilities
Capability
Secure SDLC
Supporting copy
Integrate appropriate security activities throughout design, development, testing and release.
Capability
Threat Modeling
Supporting copy
Identify assets, trust boundaries and credible threats before implementation decisions are finalized.
Capability
SAST
Supporting copy
Analyze source code for relevant security weaknesses during development and CI/CD.
Capability
Dependency Scanning
Supporting copy
Identify vulnerable, outdated or unsupported third-party software components.
Capability
Secret Scanning
Supporting copy
Detect credentials and sensitive configuration before they reach shared repositories or production.
Capability
Container Security
Supporting copy
Assess container images, dependencies, runtime configuration and deployment controls.
Capability
IaC Security
Supporting copy
Validate infrastructure definitions for insecure or noncompliant cloud configurations.
Capability
Policy as Code
Supporting copy
Apply repeatable infrastructure and delivery policies through automated, reviewable controls.
Capability
CI/CD Security
Supporting copy
Add risk-based security checks and approval gates to software delivery pipelines.
Capability
Kubernetes Security
Supporting copy
Protect clusters and workloads through RBAC, secrets, policies and controlled network exposure.
Capability
Cloud Identity
Supporting copy
Apply least-privilege access and workload identities across cloud environments.
Capability
Security Observability
Supporting copy
Centralize relevant security events, deployment history, logs and operational signals.
How We Deliver
Assess
Map applications, pipelines, cloud environment, current controls and recurring security pain points.
Prioritize
Choose controls according to application risk and developer workflow.
Integrate
Add security tooling and policies to source, CI/CD and infrastructure workflows.
Tune
Reduce false positives and define severity-based handling.
Govern
Create exception, approval and ownership paths for findings.
Improve
Use incidents, vulnerabilities and developer feedback to evolve the controls.
Ready to Plan the Next Step?
DevSecOps Technology Stack
5.0 REVIEWS
Source & CI/CD
Application Security
Containers
Infrastructure
Cloud
Identity & Secrets
Observability
Testing
Application Security Automation
Static Analysis
Scan source for relevant implementation weaknesses.
Dependency Risk
Track vulnerable or unsupported components.
Secret Detection
Catch credentials before they reach production.
IaC Validation
Review infrastructure definitions before deployment.
API Security
Test authentication, authorization and common API risks.
Exception Workflow
Document accepted risk and remediation ownership.
Integrations & Connected Systems
Repositories
GitHub | GitLab | Azure DevOps
CI/CD
GitHub Actions | GitLab CI | Azure Pipelines | client tooling
Cloud
AWS | Azure | Google Cloud
Containers
Registries | Kubernetes platforms
Issue Tracking
Jira / client ticketing for remediation workflow
Security Tooling
Client-selected SAST, SCA, DAST, secrets and cloud security platforms
Engagement Model
Security & Governance
Security automation should improve engineering decisions rather than create a false promise of security through tooling alone.
Identity & Access
Least privilege and role-aware access.
Secrets
Keep credentials out of code and unmanaged configuration.
Data Protection
Protect sensitive data according to workload requirements.
Environment Boundaries
Separate development, staging and production appropriately.
Auditability
Keep useful deployment and operational history.
Recovery
Plan backup, rollback and incident paths according to business impact.
DevSecOps does not eliminate application-security risk. Automated controls need appropriate configuration, ownership and human review, and they should complement secure architecture, code review, penetration testing and incident response according to the application's risk profile.
Why Choose Virtual Coders for DevSecOps?

"Game-Changing Custom SaaS Solutions – Highly Recommended! Working with Virtual Coders to develop our custom SaaS platform was transformative. Their team grasped our unique needs and delivered a robust solution, greatly enhancing our operations. Their attention to detail and proactive communication made the process smooth and enjoyable. Highly recommended for Australian companies seeking to enhance their software solutions!"
Rick Giesel
Owner, ICT
Why Choose Virtual Coders for DevSecOps?
✓Full-stack application + platform engineering perspective.
✓Architecture choices connected to real product and operational requirements.
✓Cloud, DevOps, API, data and integration capability in one delivery team.
✓Incremental modernization rather than unnecessary rewrites.
✓No unsupported certification, compliance or performance claims.
Frequently Asked Questions

Want Security Checks Inside Your Delivery Workflow?
DevSecOps services integrate security practices and automated checks into software development, CI/CD, infrastructure and cloud operations so teams receive security feedback throughout delivery.
DevOps focuses on collaboration and software delivery across development and operations. DevSecOps makes security an explicit part of those workflows through shared ownership, automation and risk-based controls.
Depending on the stack, checks may include static analysis, dependency scanning, secret detection, container/image scanning, IaC validation, policy checks and selected dynamic or API testing.
No. Blocking rules should consider severity, confidence, exploitability, environment and business risk. Poorly tuned gates can create alert fatigue and encourage bypasses.
Yes. DevSecOps for Kubernetes can include image controls, RBAC, secrets, policy, IaC checks and deployment validation alongside broader cluster security.
Yes. Cloud security automation can use provider capabilities plus CI/CD and policy tooling according to the client's cloud environment.
No. Automated pipeline controls and penetration testing address different parts of the security lifecycle. High-risk applications may require both, along with architecture review and secure development practices.
Yes. The goal is usually to integrate and tune the client's existing or selected tools rather than replace a functioning toolchain without reason.
SEND US A MESSAGE.

READY TO ACCELERATE YOUR TECH JOURNEY?
Partner with our expert engineers to transform your ideas into scalable, high-performance solutions tailored to your business needs.
OUR OFFICES
India
E-414 to 416, Ganesh Glory 11, Jagatpur Road, Nr. BSNL Office, off. S.G. Highway, Jagatpur, Ahmedabad, Gujarat - 382470
Australia
18, Giancarlo Crescent, Doolandella-4077, QLD, Australia
Canada
20 Meadowglen Pl, Toronto, ON M1H 2Y5